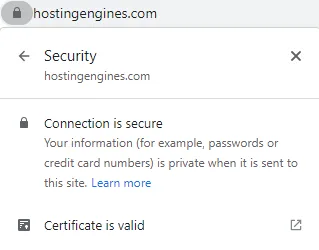
When you go to a website that uses an SSL certificate, your browser shows a small icon on the left side of the address bar. For years that was a padlock. Chrome swapped it for a neutral “tune” (settings) icon in version 117 back in 2023, while most other browsers still show a lock. Either way, it means the connection between you and the site is encrypted, so what you type can’t be read along the way.
The padlock became a symbol of trust and security because the SSL certificate makes an encrypted connection between the user and the website possible. One honest warning, though: it only proves the connection is private, not that the site itself is honest. Phishing sites can get certificates too, which is exactly why Google retired the lock icon in Chrome.
Since Google keeps pushing the web toward HTTPS, an SSL certificate is no longer optional. Chrome has labeled every plain HTTP page “Not secure” since 2018, and Google said Chrome 154 (October 2026) turns on “Always Use Secure Connections” by default, so visitors get a warning before an HTTP-only public site even loads. Without a certificate, your visitors’ data is exposed in transit and many of them will simply leave.
So, what is SSL, and why should you install it? In this in-depth guide, we’ll walk you through everything you need to know about SSL certificates. Let’s start with the basics.
Read also what is CDN?
What is an SSL certificate?
The internet is an open network. Data travels through many routers and networks on its way from your browser to a website, and without encryption anyone along that path could read it.
With the internet becoming more and more popular and the need for more information, the need for SSL certificates is becoming more and more relevant.
An SSL (secure sockets layer) certificate is the foundation of the security of any website. It’s a small digital file, issued by a trusted company, that ties a website’s domain name to a cryptographic key. Browsers use it to confirm they’re talking to the real site and to set up an encrypted connection.
A quick note on names: the original SSL protocol is long gone. Its successor, TLS (Transport Layer Security), has been the standard since 1999, the old SSL 3.0 was officially deprecated in 2015, and today’s sites run TLS 1.2 or TLS 1.3. People still say “SSL certificate” out of habit, and the certificates themselves work with TLS. For the full story, see our guide on SSL/TLS certificates and how they work.
The certificate proves that the website you’re connecting to is who it says it is, thanks to a digital signature from the authority that issued it.
The SSL certificate is usually provided by the website. If you want to use a secure connection, you’ll need to verify the website that you are connecting to has a valid SSL certificate.
These certificates are usually issued by a certificate authority and they are made to be compatible with all types of browsers across the world, which makes it easier for the website to use them.
They are the most widely supported form of digital certificate and are used by the majority of websites on the web.
Important terminologies SSL-related:
Before we dig deep into this topic, you need to know some phrases and terminologies to help you fully understand what are SSL certificates all about. These terminologies are often used by SSL certificate experts.
Certificate Authority CA:
The certificate authority is an entity that issues and manages certificates, which are digital identification. The CA is a trusted third party that ensures that the public key belongs to the entity that claims it.
Root Certificate:
The root certificate sits at the top of the chain of trust. It’s trusted by default because it ships with your browser or operating system, and it’s used to check the signatures on the certificates below it, all the way down to the website’s own SSL certificate.
Public Key:
The web server public key “sometimes called a public encryption key” is a long string of numbers that the server shares openly. It’s included in the SSL certificate, and the browser receives it when it starts a connection with the web server.
Since anyone can see it, the public key alone can’t unlock anything. Its job is to let the browser check that the server really holds the matching private key.
Private key:
The web server’s private key is the secret half of the pair. It never leaves the server. The server uses it to prove its identity during the connection (by signing data that the browser checks with the public key) and, in older setups, to decrypt the key material the browser sends.
If the private key is lost, the certificate is useless and has to be reissued. If it’s stolen, the certificate should be revoked right away, because someone else could impersonate the site.
Secret key:
The secret key (also called the session key) is a symmetric key that the browser and the server agree on for one visit. Both sides use the same key to encrypt and decrypt everything they send each other, which is much faster than using the public and private keys for all the traffic.
Certificate authority digital signature:
The certificate authority’s digital signature is a digital signature that is attached to a digital certificate. The certificate authority digitally signs the certificate, which is then used by web browsers to verify the identity of the website it is connecting to.
Now that we have defined some terms, we can now start breaking down the topic by first knowing how SSL certificates work.
How do SSL certificates work?
When a web browser and the web server connect and the encrypted link is established, the browser sends and receives information from the web server.
Before any real data is sent, the two sides run a quick “handshake” to check the certificate and agree on a secret key.
Firstly, when you click on a website your web browser initiates a connection with the web server and asks it to verify its identity.
Secondly, the server responds to the web browser and sends the SSL certificate and the public key.
Then the browser verifies the identity of the server by checking the certificate authority’s signature on the SSL certificate against the root certificates installed in the browser. It also checks that the certificate hasn’t expired and matches the domain you typed.
Next, the browser and the server agree on a shared secret key. In older versions of the protocol, the browser created it, encrypted it with the server’s public key and sent it over. Modern TLS 1.3 uses a key exchange (Diffie-Hellman) where both sides work out the same secret without ever sending it, and the server signs the exchange with its private key to prove who it is.
Either way, the private key never leaves the server, and only the real server can complete this step.
Finally, the web server and the web browser both hold the same symmetric secret key, and they use it to encrypt and decrypt everything they send each other for the rest of the visit.
Once that happens, the process is complete and the communication between the browser and website is safe and secure.
Although this process has several steps, it happens in milliseconds, long before you notice it.
What information does an SSL certificate have?
The certificate contains information about the website and its owner. This information is displayed in the certificate and includes the following:
- Domain name
The domain name is the name of the website to which the SSL certificate has been issued. And it is the first part of SSL certificates.
- digital signature.
A signature is created by a certificate authority to sign the digital certificate. A digital signature is an assurance that the data has not been changed since it was signed. The digital signature is generated by a Certificate Authority (CA) in an SSL certificate.
- Associated subdomains.
Associated subdomains are web addresses that have a relationship with the main domain.
- Date of issue of SSL certificate.
The date of issue of an SSL certificate is the date that a security certificate is issued from a Certificate Authority.
- The expiration date of the SSL certificate.
The expiration date is the date the certificate stops being valid. Lifetimes keep getting shorter: public certificates were capped at 398 days from 2020, the cap dropped to 200 days on March 15, 2026, and it will fall to 100 days in March 2027 and 47 days in March 2029. Free Let’s Encrypt certificates last 90 days.
- The public key
The public key is used to encrypt the connection between the browser and the website.
- The Address.
- The Country.
- The State.
- The City.
When you click on the lock button you will see some of this information.
What is the purpose of SSL certificates?
SSL certificates encrypt the data transmitted by your website. They ensure that no one can intercept and read the information between a website and visitors.
The purpose of SSL certificates is to ensure that your connection is secure. When you connect to a website, your connection is encrypted by the website, and only the website can decipher it.
But encryption alone isn’t enough. You also need to know who is on the other end, and that’s the certificate’s second job: it tells your browser that the website is who it says it is, so you’re not encrypting your data straight to an impostor.
Why do websites need SSL certificates?
An SSL certificate is the foundation of the security of any website. In the following three points we will shed some light on why websites need an SSL certificate:
Firstly: SSL Boost the website security
All SSL certificates are used to encrypt traffic between your web browser and your website’s server. SSL certificates are an especially useful tool for protecting your website from man-in-the-middle attacks.
What is a man-in-the-middle attack?
A man-in-the-middle attack is when an attacker intercepts unencrypted communication between your computer and your website’s server. This attack can potentially give the attacker access to sensitive information like passwords, credit card information, and personal data.
The most common reason websites need SSL certificates is to prevent hackers and malicious bots from stealing information.
Secondly: Improve SEO
An SSL certificate not only gives you better security but can also help a little with your rankings and overall SEO.
Search engine optimization is the process of improving the ranking of a website in search engine results. Google announced HTTPS as a ranking signal back in 2014, though it called it a lightweight one, and great content still matters far more. Google’s page experience guide still asks whether your pages are “served in a secure fashion”.
When your website has an SSL certificate, it is encrypted, making it more difficult for hackers to read the contents of your website as well as the website becomes more trustworthy and trusted different from a website without one.
So, an SSL certificate gives you a small direct boost at best. The bigger SEO benefit is indirect: visitors don’t bounce away from a “Not secure” warning, and they trust your site enough to stay. We dig into this in does an SSL certificate boost your ranking.
Another benefit is that Google prefers to show the HTTPS version of a page when both versions exist, so switching to HTTPS keeps your preferred URLs in the results.
Thirdly: Gaining the user’s trust
When you visit a website, you may be entering data such as your name, e-mail address, or credit card information. That information is what websites need to collect for their purposes.
On the other hand, the visitor’s browser may not trust the site, and the visitor will be presented with a warning that their personal information is not secured.
Websites have to have a security certificate in place so that the information they collect isn’t intercepted by hackers. Websites need to have SSL certificates to protect their users’ privacy and prevent their information from being stolen.
Read also, what is Uptime?
What are the types of SSL certificates?
There are different types of SSL certificates, and you need to understand the differences to know which one is right for your business. Here’s what you need to know.
The type of SSL certificate is divided depending on 2 factors:
- The validation
- The number of domain
The types of SSL certificates according to the validation:
Domain Validation:
Domain validation SSL certificates provide validation for a domain name. This means the certificate is designed to confirm that the domain name you are trying to secure is owned by the organization or individual with which you have an agreement.
The check is usually automatic: you prove you control the domain by adding a DNS record, uploading a file or clicking an email link, and the certificate is issued in minutes. Domain validation certificates are for everyone, individuals and businesses alike, and they’re what free providers like Let’s Encrypt issue.
Organization validation:
An Organization Validation certificate is a type of SSL certificate that can be used to verify the organization behind a website, the registration of the business, and the domain name.
The certificate authority checks that the organization legally exists (for example, through official business registries) before issuing it. Organization validation SSL certificates are for registered organizations, not for individuals.
Extended validation:
An extended validation SSL certificate has the strictest identity checks of the three. The encryption itself is the same strength as a DV or OV certificate; what you pay for is the deeper vetting of the company behind the site.
To be issued an extended-validation SSL certificate, the applicant will have to provide their legal business name, type of business, and physical address to the certificate provider.
After the certificate authority checks the information they will compare it with the information collected by a third party for Extended Validation.
This type of certificate is never free, and it’s only issued to legally registered organizations (private companies, government bodies and similar entities), not to individuals. Keep in mind that browsers stopped showing the old green address bar with the company name in 2019, so most visitors can’t tell an EV certificate apart from a free one anymore.
The types of SSL certificates according to the number of domains:
Single domain:
If you have only one domain, a single-domain SSL certificate is all you need. It’s the simplest type of SSL certificate, and it encrypts traffic just as strongly as the bigger ones. It simply covers fewer names.
The certificate is valid for one domain name (usually both the www and non-www versions). Single-domain SSL certificates are also the cheapest type of SSL certificate.
There’s also the wildcard certificate, which covers one domain plus all of its first-level subdomains (like blog.example.com and shop.example.com) with a single certificate.
Multi-Domain:
Multi-domain SSL certificates are great for businesses with multiple websites. Instead of having a separate certificate for each website, you can get a single certificate that covers all of your websites.
They’re a bit more involved to set up, and paid multi-domain certificates usually cost more as you add names. Let’s Encrypt can also put several domain names on one free certificate, which is how many hosts cover all the domains on an account.
Unified communications:
The unified communications SSL certificate (UCC) is a multi-domain certificate made for companies that need more than a secure website. It was designed for Microsoft Exchange and Office Communications servers, so one certificate can cover the mail server, webmail and related hostnames.
These organizations could be corporations, schools, or any other group of people who must share information securely.
This type of SSL certificate costs more than a single-domain one because it covers many hostnames. It secures the connections to the company’s email and communication servers for all of its users.
The company will have to have a big enough budget to support this type of certificate.
What is a Let’s Encrypt free SSL certificate?
Let’s Encrypt lets you secure any website with an SSL certificate at no cost. It’s run by the nonprofit Internet Security Research Group (ISRG), and it’s now the largest certificate authority in the world by the number of sites it secures.
Let’s Encrypt is a certificate authority (CA), an organization that issues certificates after checking that you control a domain. It’s a free, automated, and open certificate authority, and it only issues domain validation certificates.
A lot of hosting providers are providing the Let’s Encrypt SSL certificate for free, so you won’t face any problems with SSL certificates if you choose to sign up for a hosting company that offers this feature.
A Let’s Encrypt certificate is valid for 90 days, and your host or ACME client (such as Certbot) renews it automatically before it expires. That window is shrinking: Let’s Encrypt plans to cut the default to 64 days in February 2027 and to 45 days in February 2028, so automatic renewal is a must. Also note that Let’s Encrypt stopped sending expiry reminder emails in June 2025, so if you manage certificates yourself, use a monitoring tool or our free SSL checker to keep an eye on the expiry date.
Get a free SSL certificate for your online application from Cloudflare.
What will happen when an SSL certificate expires?
When an SSL certificate expires, browsers show visitors a full-page warning that the connection is not private, because the certificate isn’t valid anymore. Most people will turn around right there.
Visitors who click through anyway are no longer protected by a valid certificate, so the browser can’t confirm they’re talking to the real site.
Furthermore, any user that is accessing the site will be unable to validate the security and privacy of the site’s content.
So, the website owner must have plans to renew the SSL certificate before it expires, but if a certificate expires, the site owner must take action to renew it, or else the site will be considered insecure.
Fortunately, renewing a certificate is easy. You get a new certificate with a new expiration date, and with free certificates from your host this usually happens automatically.
The Conclusion
SSL certificates are a crucial part of the security of any website. They prove a website’s identity, make sure you’re talking to the real site, and make the encrypted connection possible.
SSL certificates come in several types, depending on the validation level and the number of domains they cover. They can also be paid or free, depending on the certificate authority that issues them.
And no certificate lasts forever. Today the maximum is 200 days (90 days for Let’s Encrypt), and it keeps shrinking, so set up automatic renewal and check the expiry date now and then to avoid any surprises.
Want to discover more? read what is CDN?